Generative AI is accelerating productivity in areas such as procurement, legal, finance, and operations. But it is also opening up a new risk: data leaks through normal, well-intentioned use, without the need for a "hack."
Free tool: Shadow AI Checklist. 14 questions to find out if your team is using AI without control and with what data.
This is exactly what AI Trust & Safety (AI Security and Trust) addresses: policies, controls, and monitoring to ensure AI delivers value without becoming a channel for exposure.
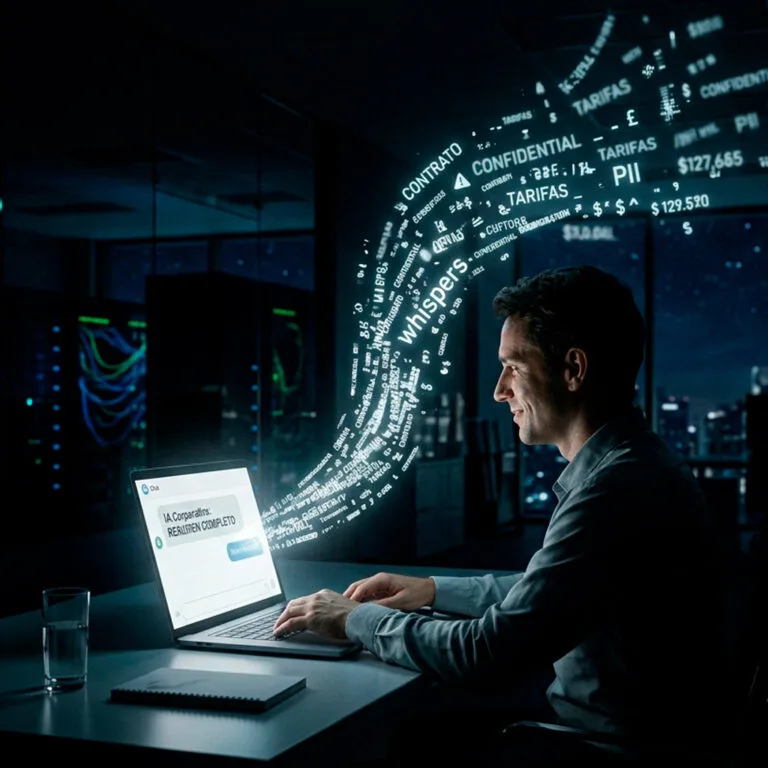
A very real example: "I just wanted a summary of the contract"
An analyst opens the corporate AI assistant and writes: "Summarize this contract and tell me the risks."
At TI Rescue, we implement AI Trust & Safety with a practical approach:
policies + DLP + Zero Trust + monitoring + exposure assessment, so that AI adds productivity without opening a silent pathway for information leakage.
To save time, copy and paste the entire document: rates, confidentiality clauses, contact data, appendices, and in some cases internal identifiers or banking information. The summary comes out perfect. The problem occurs afterwards. Depending on the tool's configuration and its integrations, that content may remain:
• stored in the chat history, • logged for support or audit purposes, • indexed for internal searches, • exposed to integrations (tickets, CRM, corporate drive) if there are no restrictions.
There was no attack. Just "productivity" without governance. And that is enough to generate exposure of sensitive information, contractual breaches, and legal risks.
What risks are you buying without realizing it?
1) Data leakage and confidentiality
Contracts, prices, agreements with suppliers, customer data, architecture, incidents, credentials "pasted by mistake."
How to prevent data leakage with DLP?
2) Shadow AI
Teams using external tools (or personal accounts) to solve tasks, taking information outside the perimeter without controls.
3) Prompt Injection (when the content "gives orders")
Documents or web pages may include malicious instructions for the assistant to ignore rules and extract more information than it should.
4) Compliance risk
If your company operates with ISO 27001 / ISO 20000 or contractual obligations, uncontrolled AI use can break information treatment and protection requirements.
Do you want us to assess your scenario (Copilot/internal LLM/corporate chat) and give you a control plan by priority?
Minimum controls to "use AI without losing control"
If you are adopting assistants like Copilot / Enterprise ChatGPT / internal LLMs, these controls are the starting point:
✅ 1) AI Usage Policy (clear and applicable)
What can be shared, what cannot, and concrete examples by area (legal, finance, HR, sales).
✅ 2) DLP for AI (input and output)
Data leakage prevention: detect and block PII, banking data, contracts, credentials, classified information.
• What is a DLP?
✅ 3) Classification + permissions by context (Zero Trust applied to AI)
The assistant should only see what the user can see and with limits: no "broad access" for convenience.
• Click here for more information on what Zero Trust is
✅ 4) Retention, audit, and traceability
Minimum necessary logs, protected and auditable: knowing what was queried, what was shared, who, and when.
✅ 5) Practical training (with real cases)
Not "generic tips": scenarios like the contract, credentials, commercial proposals, incidents, etc.
AI is not the risk: the risk is adopting it without governance
If your organization is already using generative AI, the question is not whether it is "worth it". The question is: Can your company demonstrate that it is using AI with security, confidentiality, and compliance controls?
Frequently asked questions
Topics that might interest you:
• What is CTEM (Continuous Threat Exposure Management) • IT Services • What are Non-Human Identities
Subscribe to Our Blog: Stay up to date with the latest news and tips in cybersecurity. Subscribe now.
Do you want to put your company's AI under control?
Learn about our AI and machine learning audit service: diagnosis, testing, and closure plan with evidence.
View the serviceYou may also like
Responsible AI Audit: The Guide for Companies Implementing Deep Learning and Generative Models
What are the risks of artificial intelligence?
Your AI stack as a human body: why stopping at LLM + RAG leaves it without an immune system
Comments (0)
Be the first to comment.