SOAR, or Security Orchestration, Automation, and Response, is a platform that automates repetitive security tasks to speed up incident handling. It connects your security tools, runs predefined playbooks, and helps your team respond faster to threats without manual intervention.
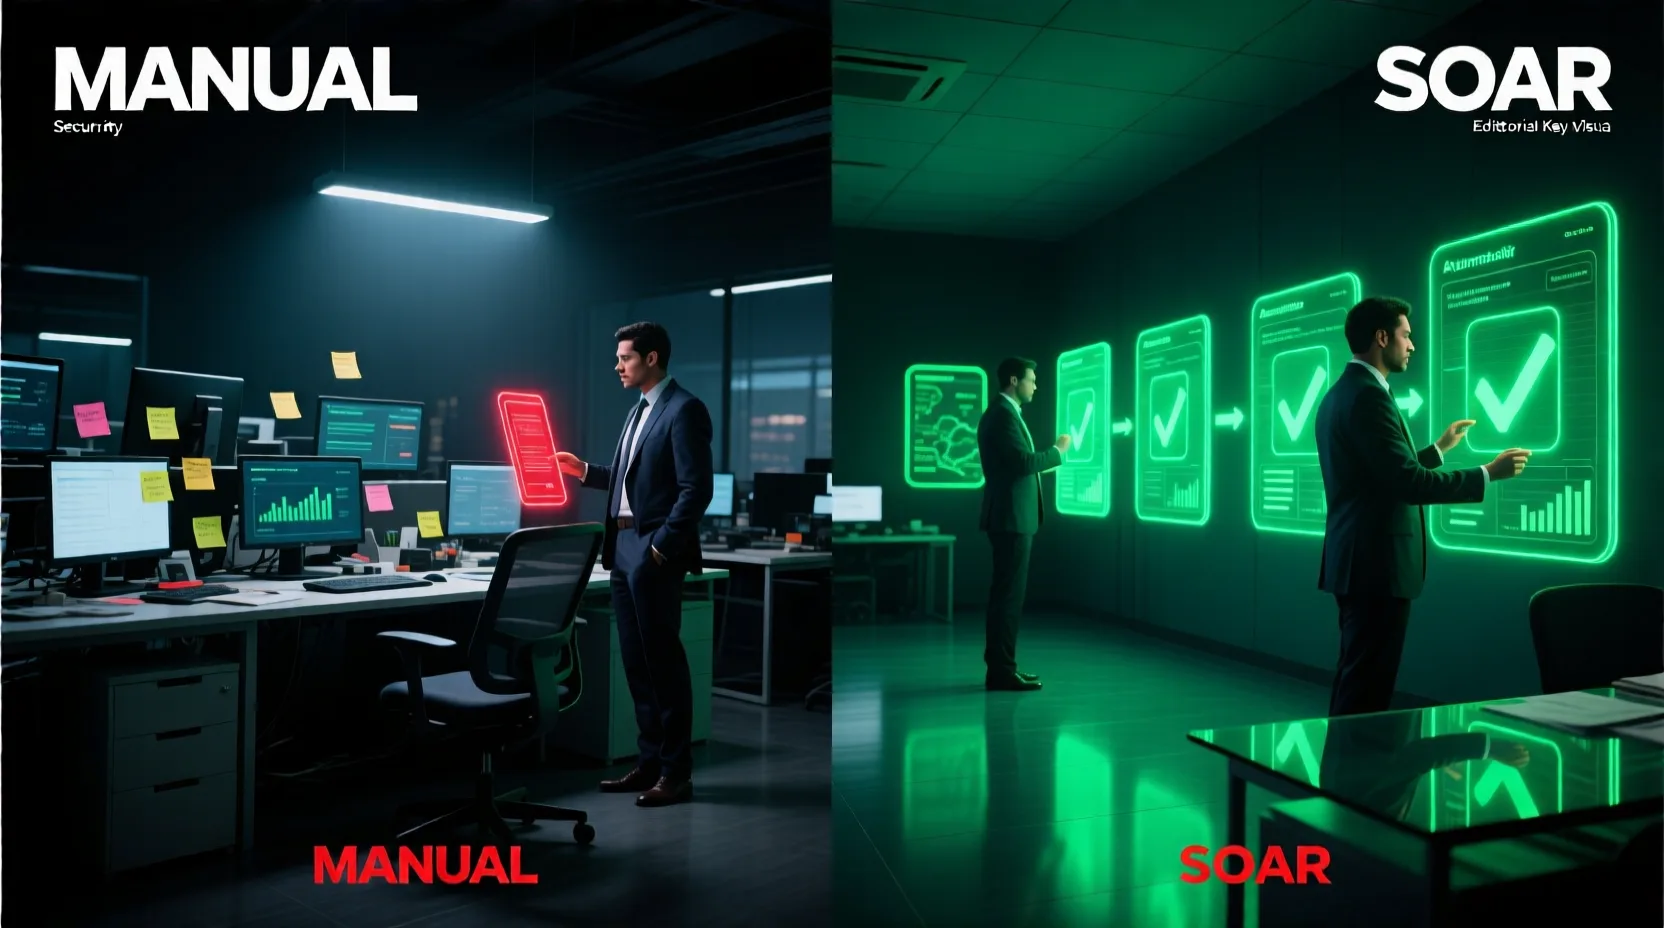
Anatomy of the attack described in the article.
Why SOAR matters for businesses in 2026
Cyber threats are evolving rapidly, and manual response times are no longer sufficient for most organizations. In 2026, the volume of alerts generated by security tools often exceeds the capacity of human analysts to process them manually. SOAR addresses this bottleneck by automating the initial triage and response steps, allowing your team to focus on complex investigations. For small and medium-sized businesses, this means fewer false positives and a more efficient use of limited security resources.
How SOAR works: orchestration, automation, and response
A SOAR platform functions through three core components. First, orchestration integrates data from various security tools like firewalls, endpoints, and email systems. Second, automation executes predefined playbooks, such as isolating an infected device or blocking a malicious IP address. Third, response provides a unified view of the incident, allowing analysts to track the progress and take final actions. This structured approach ensures that every step of the incident response process is documented and repeatable.
Measurable benefits of implementing SOAR
When should you start using SOAR?
You should consider implementing SOAR when your team spends more than 50% of its time on manual triage and repetitive tasks. Start by identifying the most common types of incidents in your environment, such as phishing emails or unauthorized access attempts. Create simple playbooks for these scenarios first, then gradually expand your automation to more complex workflows. This phased approach minimizes risk and allows your team to adapt to the new process.
How T.I. RESCUE can help your company
Implementing a SOAR platform requires careful planning and integration with your existing infrastructure. T.I. RESCUE, a Colombian cybersecurity firm based in Medellín, provides expert guidance to assess your current security posture and design a SOAR strategy tailored to your needs. We help you define the right playbooks and ensure that your team is ready to manage automated responses effectively.
Frequently asked questions
Is SOAR only for large enterprises?
No, SOAR is beneficial for businesses of all sizes, especially those with limited security staff who need to maximize efficiency.
Does SOAR replace my SIEM?
No, SOAR complements SIEM. While SIEM detects threats, SOAR automates the response to those threats.
How long does it take to implement SOAR?
Implementation time varies, but a basic setup with a few playbooks can be operational in a few weeks to a few months.
What skills are needed to manage SOAR?
You need basic knowledge of security workflows and scripting, but many modern SOAR platforms offer low-code or no-code options.
Controls and monitoring that stop the attack.
Ready to automate your security response?
Contact T.I. RESCUE, a Colombian cybersecurity company based in Medellín, to start your SOAR journey today.
Hablar con un especialistaSet this site as a preferred source on Google
You may also like
Comments (0)
Be the first to comment.